
Multi-tenant SaaS
One app, many customers, each in its own workspace.
Choose single, hybrid or multi-tenant. Each customer workspace gets its own users, sign-in, settings, secrets, connector credentials, AI keys and usage, while you run one app.
Sign-in
Their sign-in, their rules.
Each workspace signs its users in with a password, Okta or Google. Domain checks and approval modes keep the wrong people out. Your own team gets Console SSO.
- Join or create a workspace, invites, workspace admins
- Domain verification and pending-approval joins on paid plans
- IAM-style access policies enforced on the server
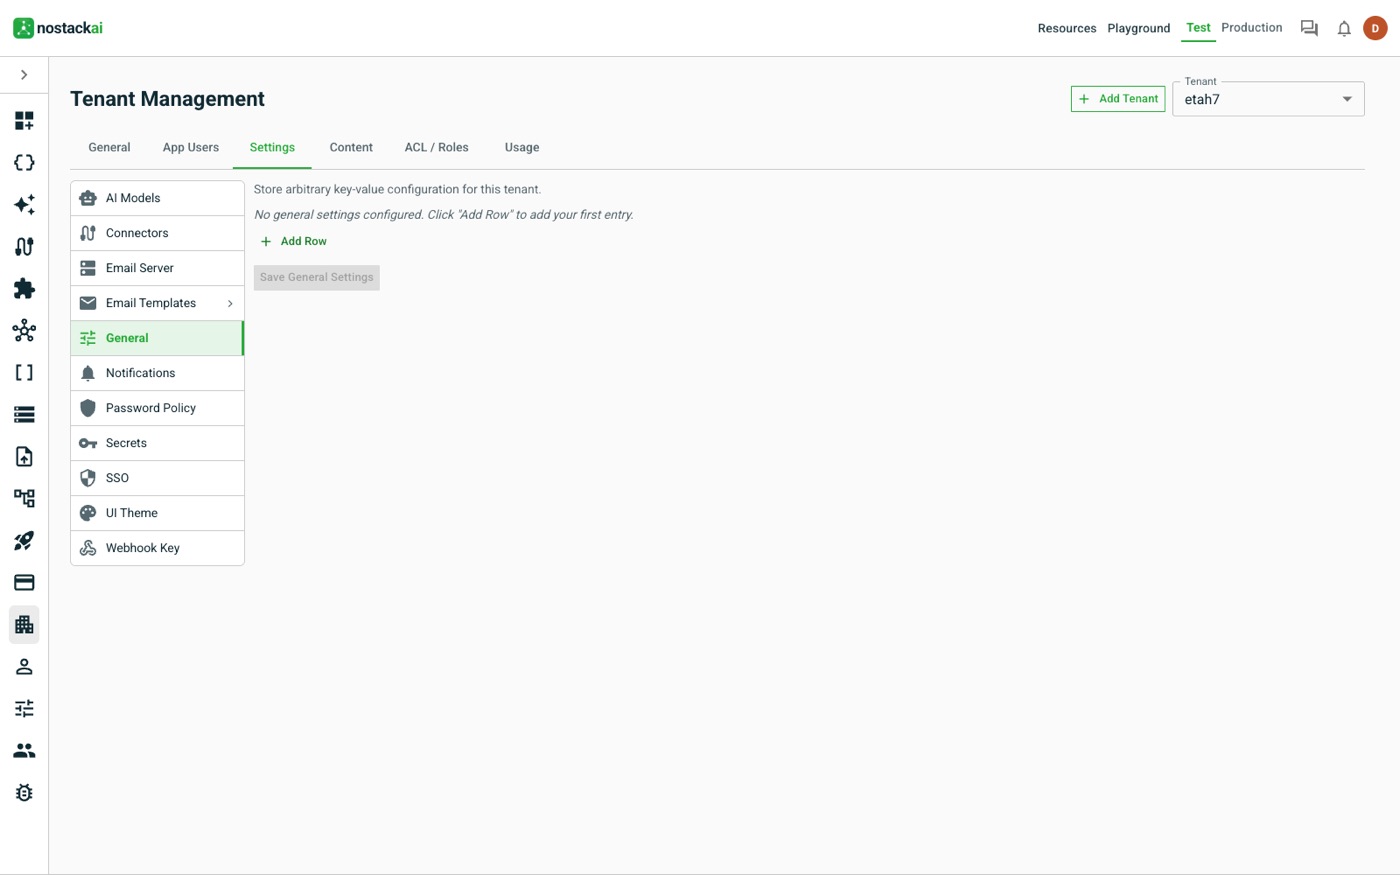
Per-workspace settings
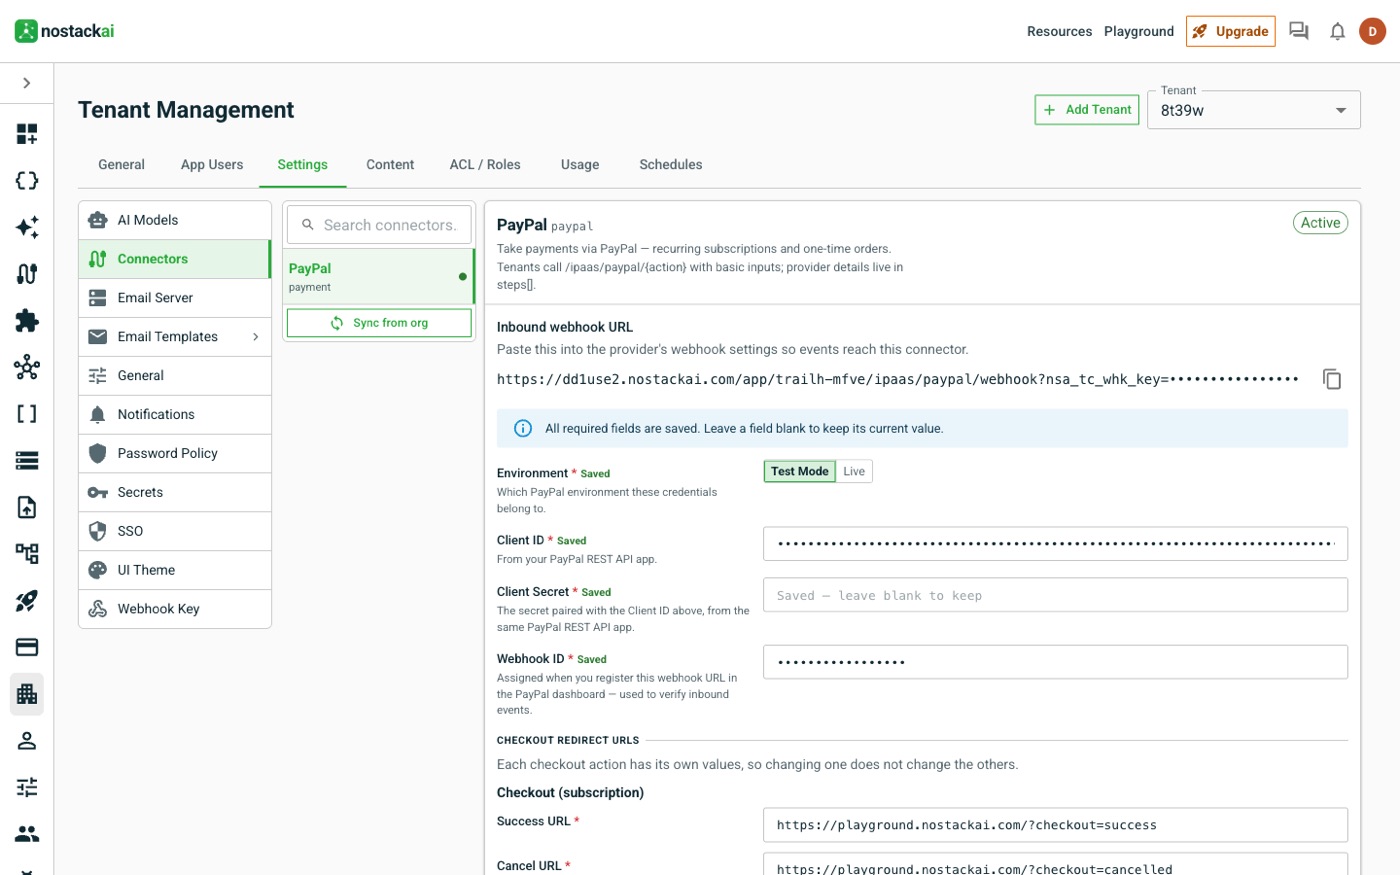
Settings and secrets per customer.
General values and encrypted secrets per workspace, read by your Logic Blocks and Glyphs at run time. Each workspace enters its own connector credentials and AI keys.
- Email templates and branding per workspace
- Feature-flag overrides per workspace
- Secrets are encrypted and never shown again
Isolation
Separate by design, dedicated if you need it.
Every org's and every workspace's data sits in its own partitions, and the server checks the scope on every request. Enterprise customers get a dedicated stack.
- Usage per workspace: API calls, records, Logic Block runs, AI tokens and cost
- Pass AI cost through to the workspace that uses it
Ready when you are
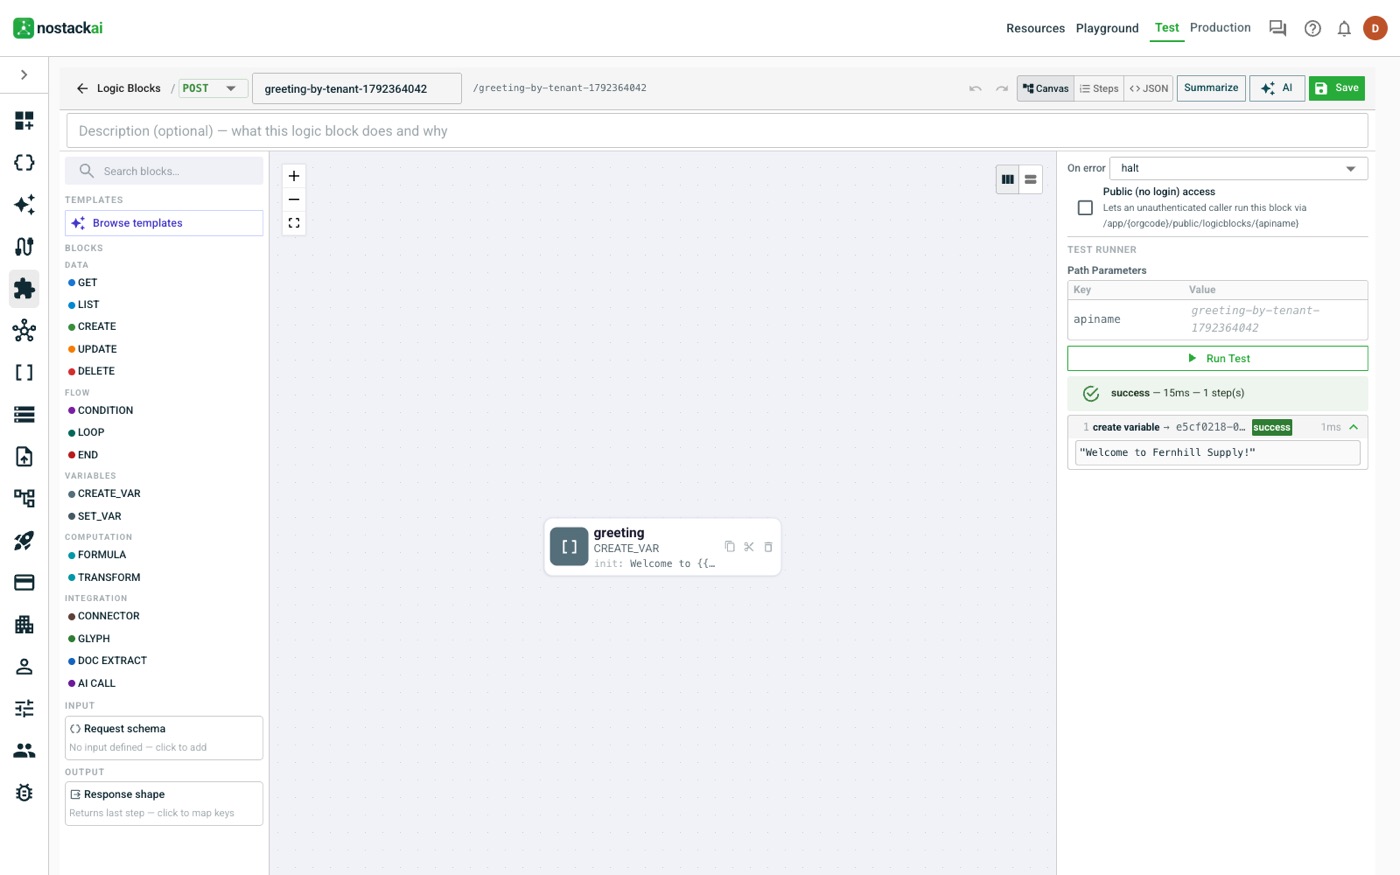
Describe it once. Run it forever.
Connect your AI client, build your backend, ship to production.